Workshop · For boards, legal, risk and compliance

AI Governance and Safety

The risks and harms of AI, the rules that now apply, and the governance framework that lets you move quickly without losing control.

Book this workshopRead the FAQ →
Length
Half day, 3½ hours
Group
Board, executives, legal, risk, IT
Led by
Judy Krieg and Simon Greenman
Covers
UK, EU and US
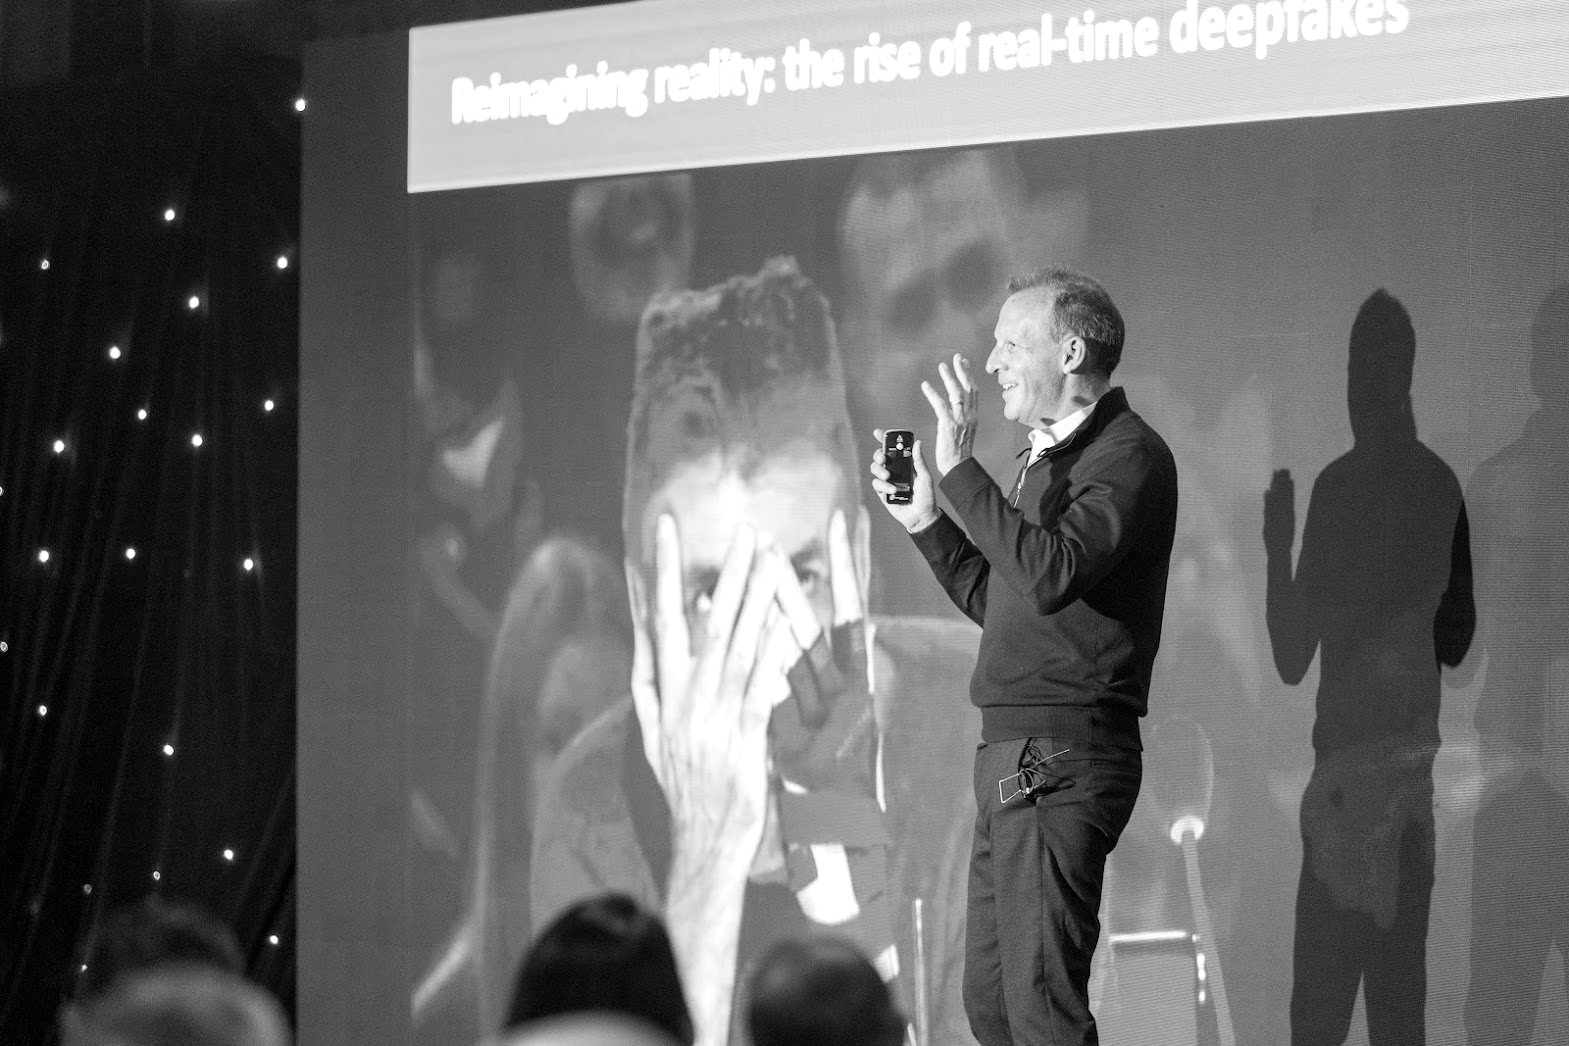
Simon Greenman presenting on real-time deepfakes
From the keynote stage: deepfakes and the new risks boards need to govern.

Risks and harms

Ten risks every organisation using AI must manage.

We take each one through real incidents, how likely it is in your business, and the controls that address it.

  1. 01Inaccuracy and invented factsConfident but wrong answers in advice, reports and customer replies.
  2. 02Bias and unfair outcomesDiscrimination in hiring, lending, pricing and service.
  3. 03Privacy and data leakagePersonal and confidential data in the wrong tools or models.
  4. 04Security attacksPrompt injection, poisoned data, and AI-enabled phishing and fraud.
  5. 05Intellectual propertyCopyright in training data and outputs; protecting your own IP.
  6. 06Lack of transparencyDecisions no one can explain to a customer, regulator or court.
  7. 07Autonomous agentsAI that takes actions, not just gives answers, without the right limits.
  8. 08Misuse and deepfakesImpersonation, manipulated content and reputational attack.
  9. 09Third-party and vendor riskLock-in, outages, changing terms and AI hidden inside suppliers' tools.
  10. 10People and over-relianceDeskilling, unchecked automation and shadow AI on personal accounts.

Regulation and standards

What the rules require, in plain English.

European Union

The EU AI Act's risk tiers: prohibited practices, high-risk systems (such as hiring and credit), transparency duties for chatbots and generated content, and rules for general-purpose models. Obligations phase in from 2025 to 2027 and reach UK firms that sell into the EU. GDPR still applies to every use of personal data.

United Kingdom

A principles-based approach applied by existing regulators: the ICO on data protection and automated decisions, the FCA for financial services, the CMA on competition and consumers. UK GDPR, the Equality Act and sector rules apply now.

United States

A patchwork of state laws (such as Colorado's AI Act and New York City's rules on hiring tools), federal agencies applying existing consumer, employment and health law, and sector rules such as HIPAA.

Standards we map to: ISO/IEC 42001 AI management systems NIST AI Risk Management Framework OECD AI Principles

The governance framework

Governance scaled to risk, not one rule for everything.

Light controls for low-risk productivity tools; full review for AI that affects customers, employees or money. The framework is practical enough to run monthly.

  1. 01
    Principles and policy

    A short acceptable-use policy and the principles behind it.

  2. 02
    Roles and oversight

    Board accountability, an AI steering group and a named owner for every system.

  3. 03
    AI register and risk tiers

    Every tool and use case recorded and rated low, medium or high.

  4. 04
    Impact assessments

    Data protection and AI impact assessments for higher-risk uses.

  5. 05
    Vendors and contracts

    Due diligence questions and contract terms for AI suppliers: data use, liability, IP and exit.

  6. 06
    Human oversight and agents

    Levels of autonomy, and when a human must be in, on or out of the loop.

  7. 07
    Transparency

    Telling customers and staff when AI is used, including AI explainability statements.

  8. 08
    Monitoring and incidents

    Measuring quality over time, and a plan for when something goes wrong.

The agenda

Three and a half hours.

  1. 0:00 15 min

    Why governance now

    What has changed, what boards are being asked, and recent incidents.

  2. 0:15 45 min

    The risks and harms of AI

    The ten risks, each with real cases and the questions to ask of your own AI.

  3. 1:00 40 min

    Regulation and standards

    The EU AI Act, the UK approach, US state and sector rules, and ISO 42001 and NIST, mapped to where you operate.

  4. 1:40 15 min

    Break

  5. 1:55 40 min

    The governance framework

    The eight building blocks, including agents and vendor contracts, and how to run them without slowing the business.

  6. 2:35 40 min

    Exercise: risk-tier your own AI

    In small groups, take your real tools and use cases, rate each for risk, and agree the controls each one needs.

  7. 3:15 15 min

    The board's role and next steps

    The questions directors should ask, and a 90-day plan.

What you leave with

AI risk registerYour tools and use cases, rated, with owners.
Policy frameworkAn acceptable-use policy and control checklist to adapt.
Regulatory mapWhich rules apply to you, and when.
Vendor checklistDue diligence questions and contract clauses for AI suppliers.
90-day planAnd a short briefing note for the board.

Built on our work with the World Economic Forum on AI leadership, and on the first AI explainability statements reviewed by the UK Information Commissioner's Office, delivered with Best Practice AI.

Best Practice AI →

Book an AI Governance and Safety workshop.

Send us a message → [email protected] → For all staff: Using AI Safely, Well and Accurately →

Talk to us

Tell us where you are on the AI journey. One of the team will reply within two working days.

We use your details only to reply to your enquiry. See our privacy notice.