Services · Adopt & govern
AI adoption and governance consulting
Make it stick and keep it safe. Change management for the people side of AI, and proportionate governance alongside it: policy, an AI register, risk tiers and human oversight, aligned to the EU AI Act and UK guidance.
Governance
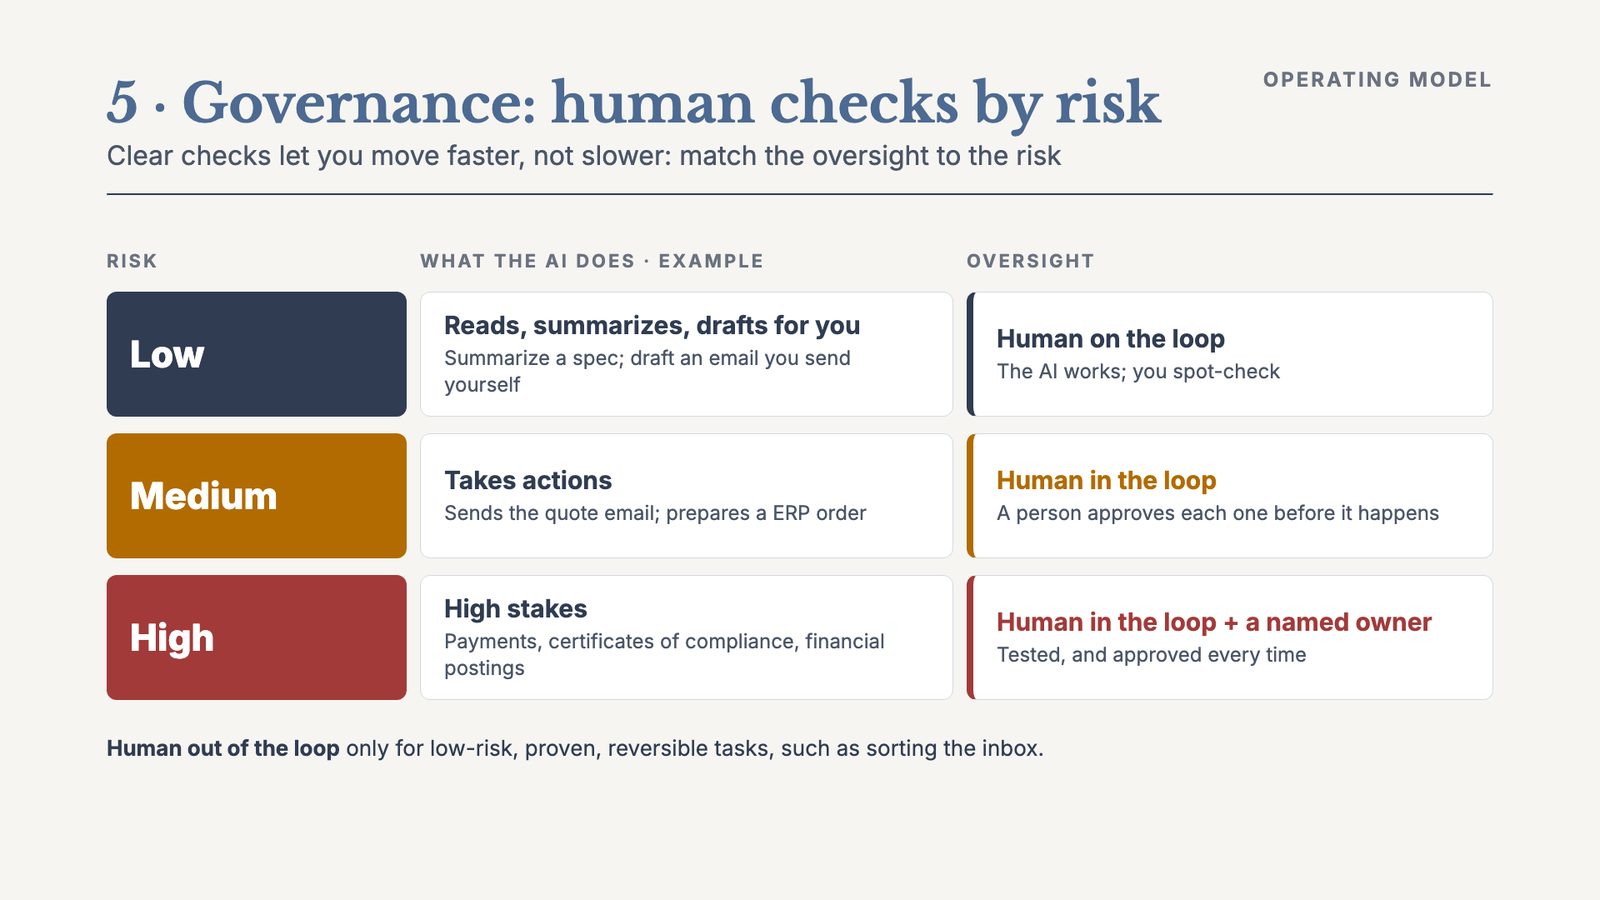
Governance scaled to risk, not one rule for everything.
Light controls for low-risk productivity tools; full review for AI that affects customers, employees or money. The framework is practical enough to run monthly.
- 01
Principles and policy
A short acceptable-use policy and the principles behind it.
- 02
Roles and oversight
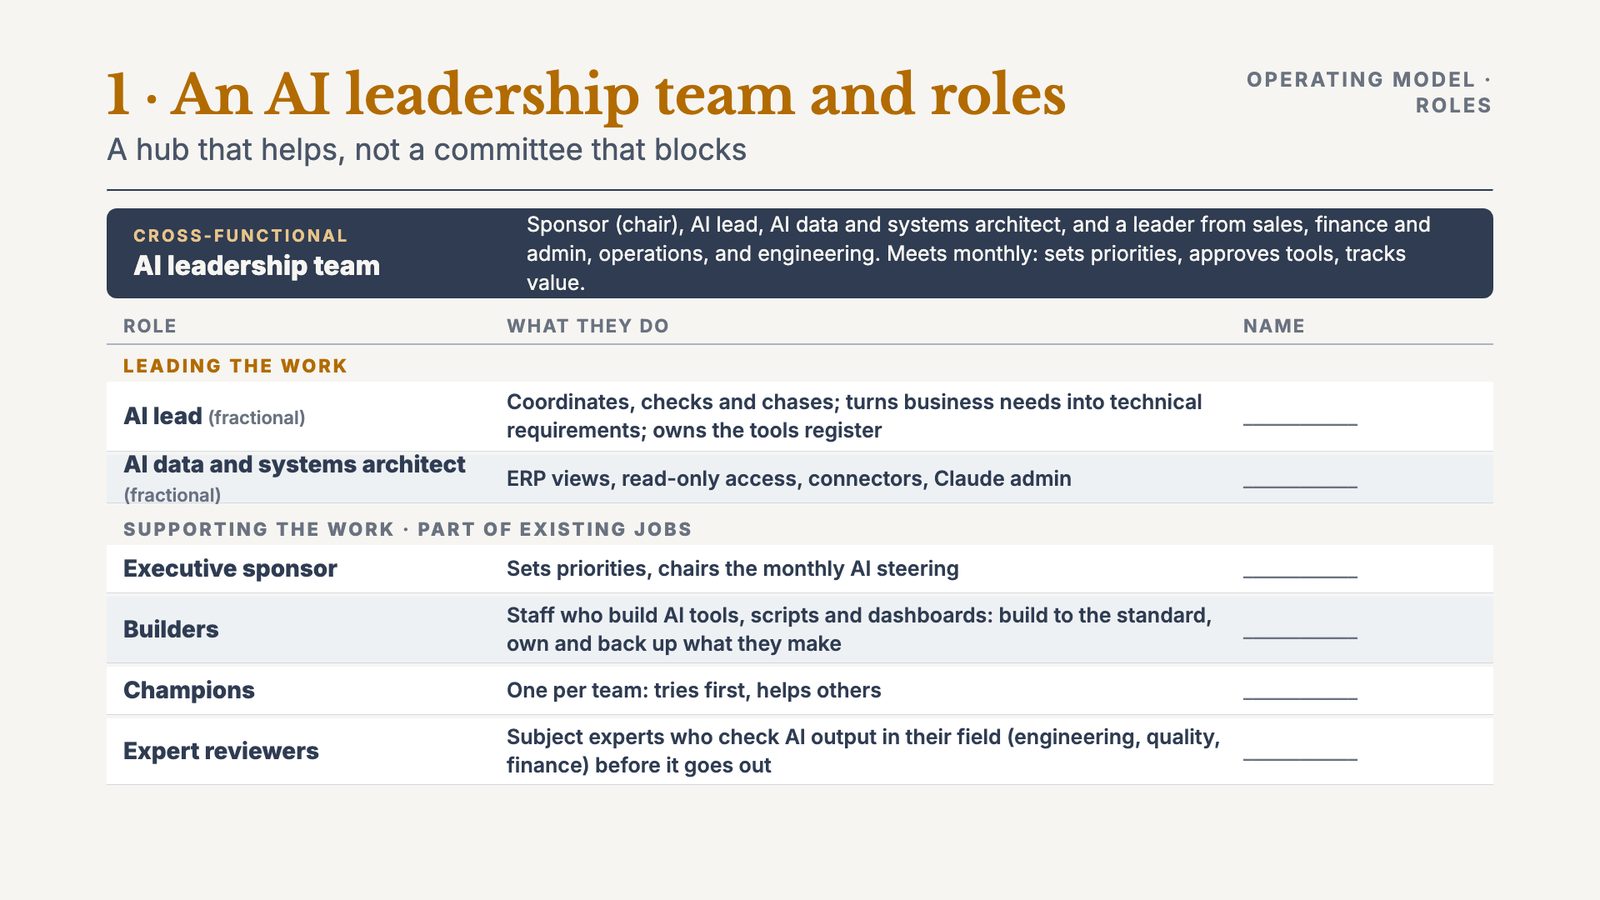
Board accountability, an AI steering group and a named owner for every system.
- 03
AI register and risk tiers
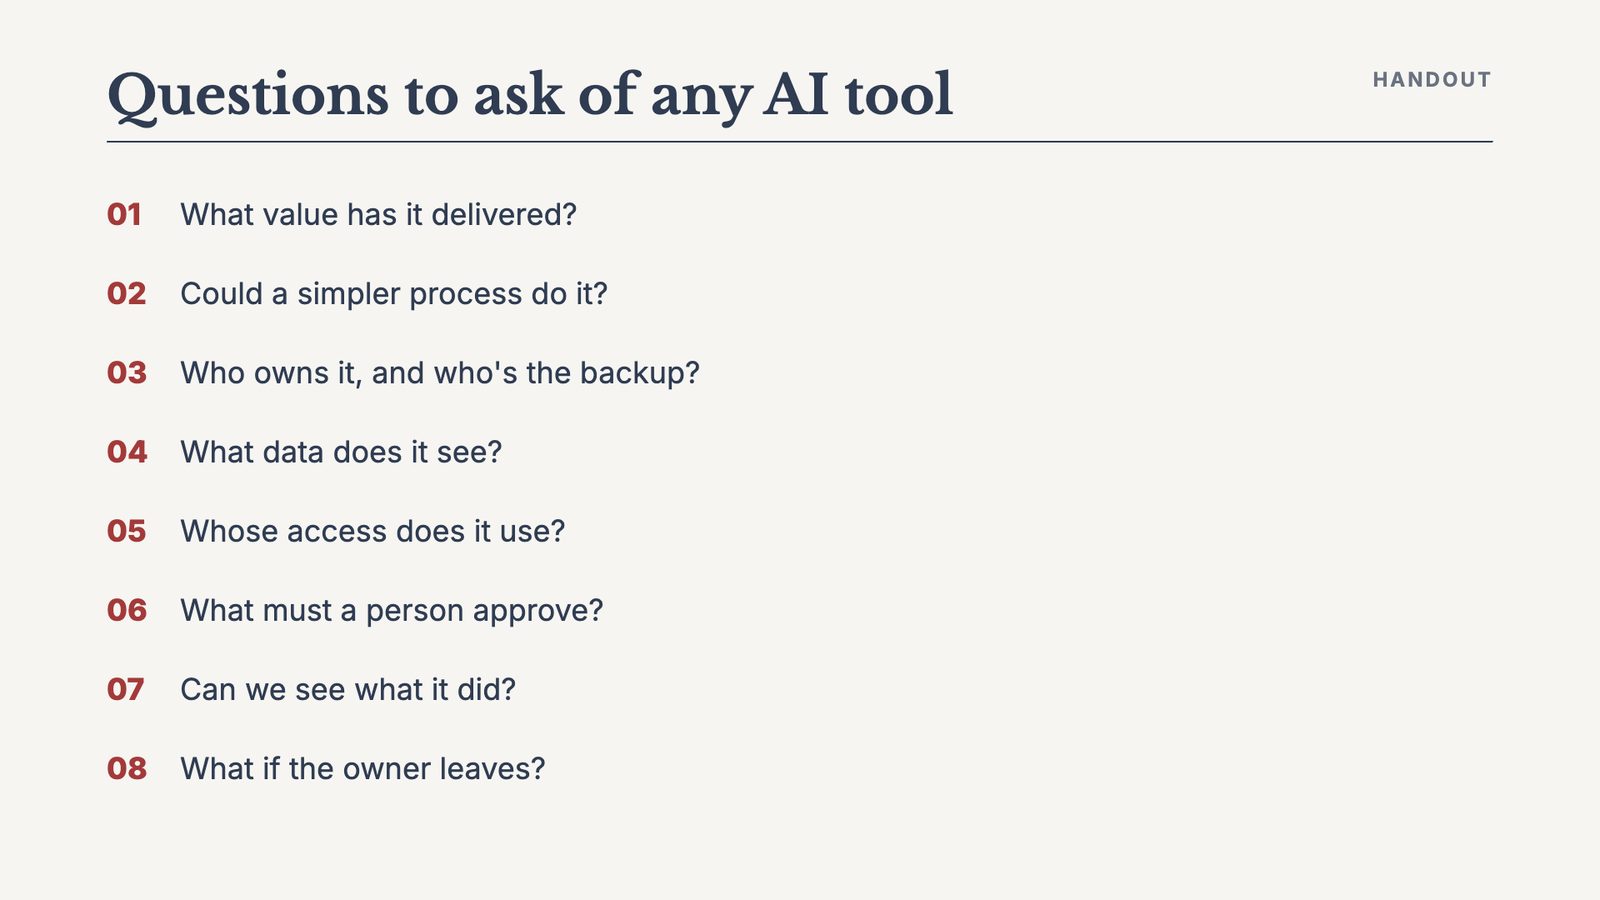
Every tool and use case recorded and rated low, medium or high.
- 04
Impact assessments
Data protection and AI impact assessments for higher-risk uses.
- 05
Vendors and contracts
Due diligence questions and contract terms for AI suppliers: data use, liability, IP and exit.
- 06
Human oversight and agents
Levels of autonomy, and when a human must be in, on or out of the loop.
- 07
Transparency
Telling customers and staff when AI is used, including AI explainability statements.
- 08
Monitoring and incidents
Measuring quality over time, and a plan for when something goes wrong.
Regulation and standards
What the rules require, in plain English.
- 01
EU AI Act
Risk tiers from prohibited practices to high-risk systems such as hiring and credit, transparency duties for chatbots and generated content, and rules for general-purpose models. Obligations phase in from 2025 to 2027 and reach UK firms that sell into the EU.
- 02
United Kingdom
A principles-based approach applied by existing regulators: the ICO on data protection and automated decisions, the FCA for financial services, the CMA on competition and consumers. UK GDPR, the Equality Act and sector rules apply now.
- 03
United States
A patchwork of state laws, federal agencies applying existing consumer, employment and health law, and sector rules such as HIPAA.
- 04
Standards we map to
ISO/IEC 42001 AI management systems, the NIST AI Risk Management Framework and the OECD AI Principles.
Adoption
Make AI part of how the work gets done.
Most of the value of AI depends on people changing how they work. We treat adoption as a programme with its own owner and measures.
- 01
Champions in every team
Named people who build, share and support, backed by ongoing coaching.
- 02
Showcases of colleagues’ wins
Peers proving it, not consultants: the fastest way to spread what works.
- 03
A tools register
Every tool staff build recorded, owned and maintained, with shared repositories.
- 04
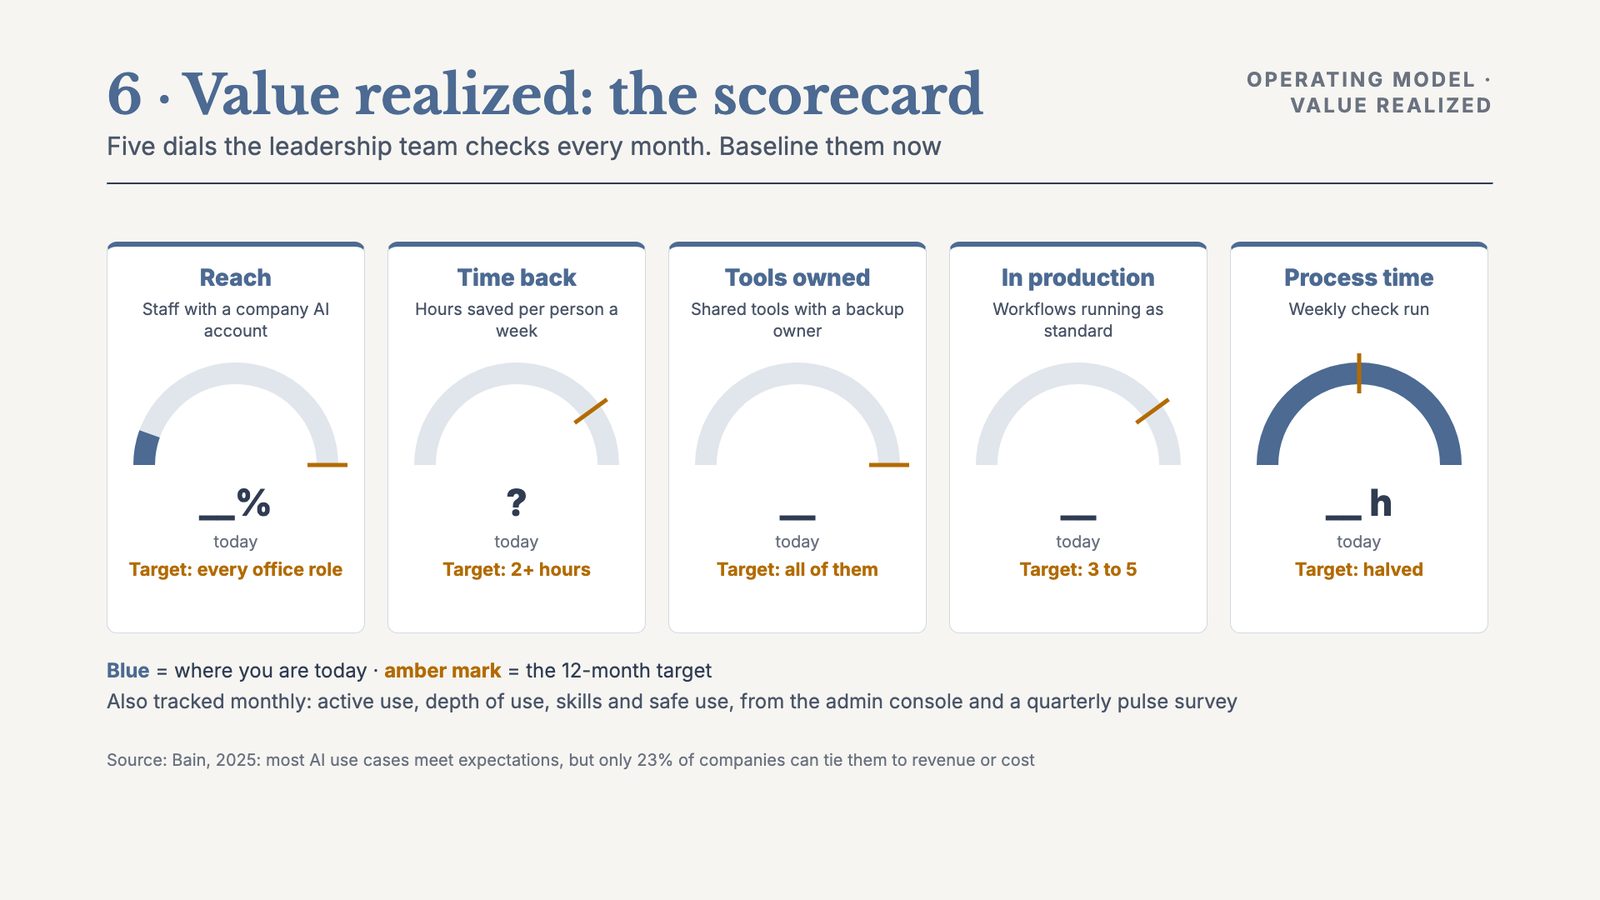
Measured adoption
Usage and value tracked on a scorecard for the board, with an AI budget line and a simple spend dashboard.
Where to start
Led by governance, legal and risk specialists.
Our governance work is led by a UK and US lawyer and IAPP-certified AI Governance Professional, with decades of experience in regulation, compliance and enforcement.
AI Governance and Safety Workshop →
Half a day for boards, legal and risk: ten AI risks, the rules in the UK, EU and US, and the framework.
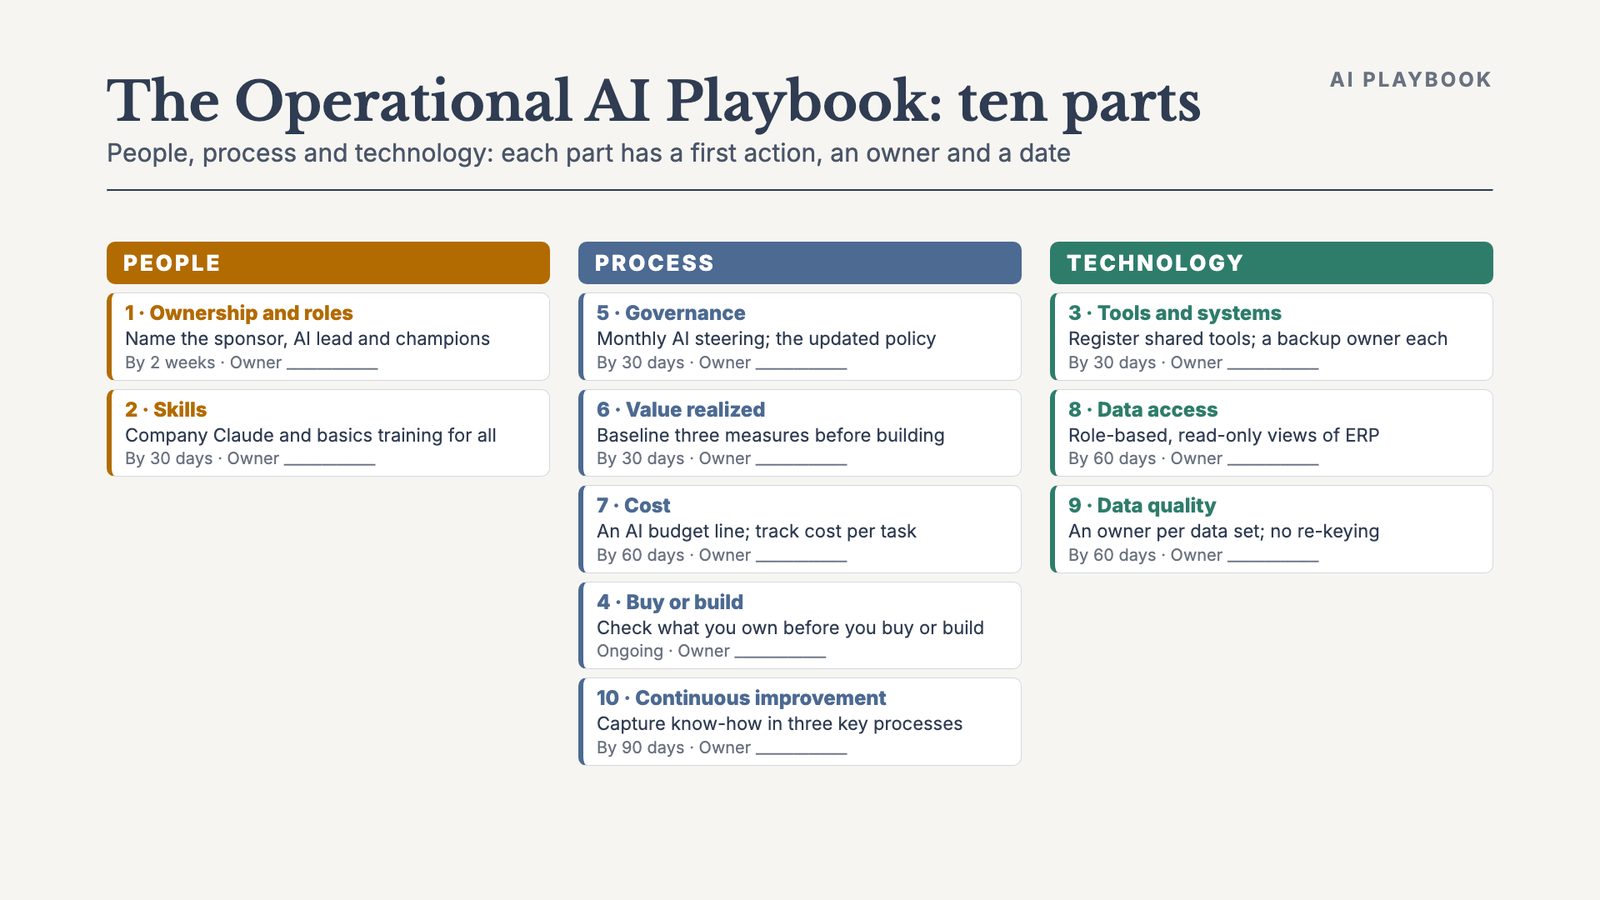
The Operational AI Playbook →
Ownership, skills, tools, governance by risk, data foundations, value and cost, with a 30/60/90-day plan.
Governance and policy questions →
Security, privacy, compliance and risk, answered.
Inside the framework
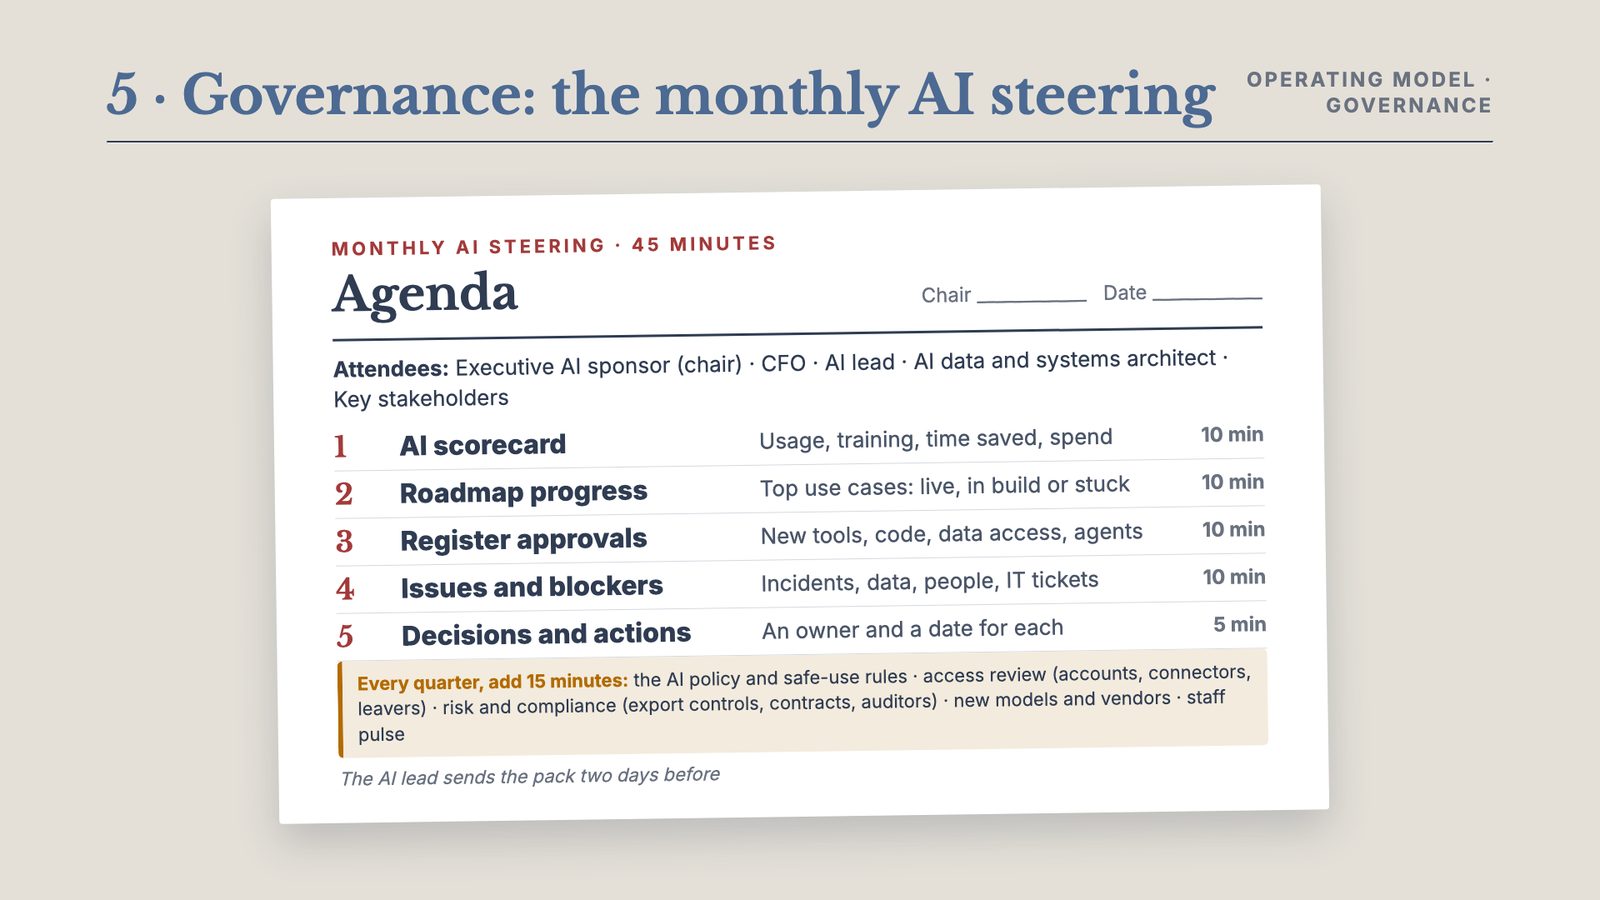
Governance your leadership team can actually run.
Our services